How to use CrowdSec IP reputation over TAXII: Sentinel, Entra ID, SIEMs and fraud checks
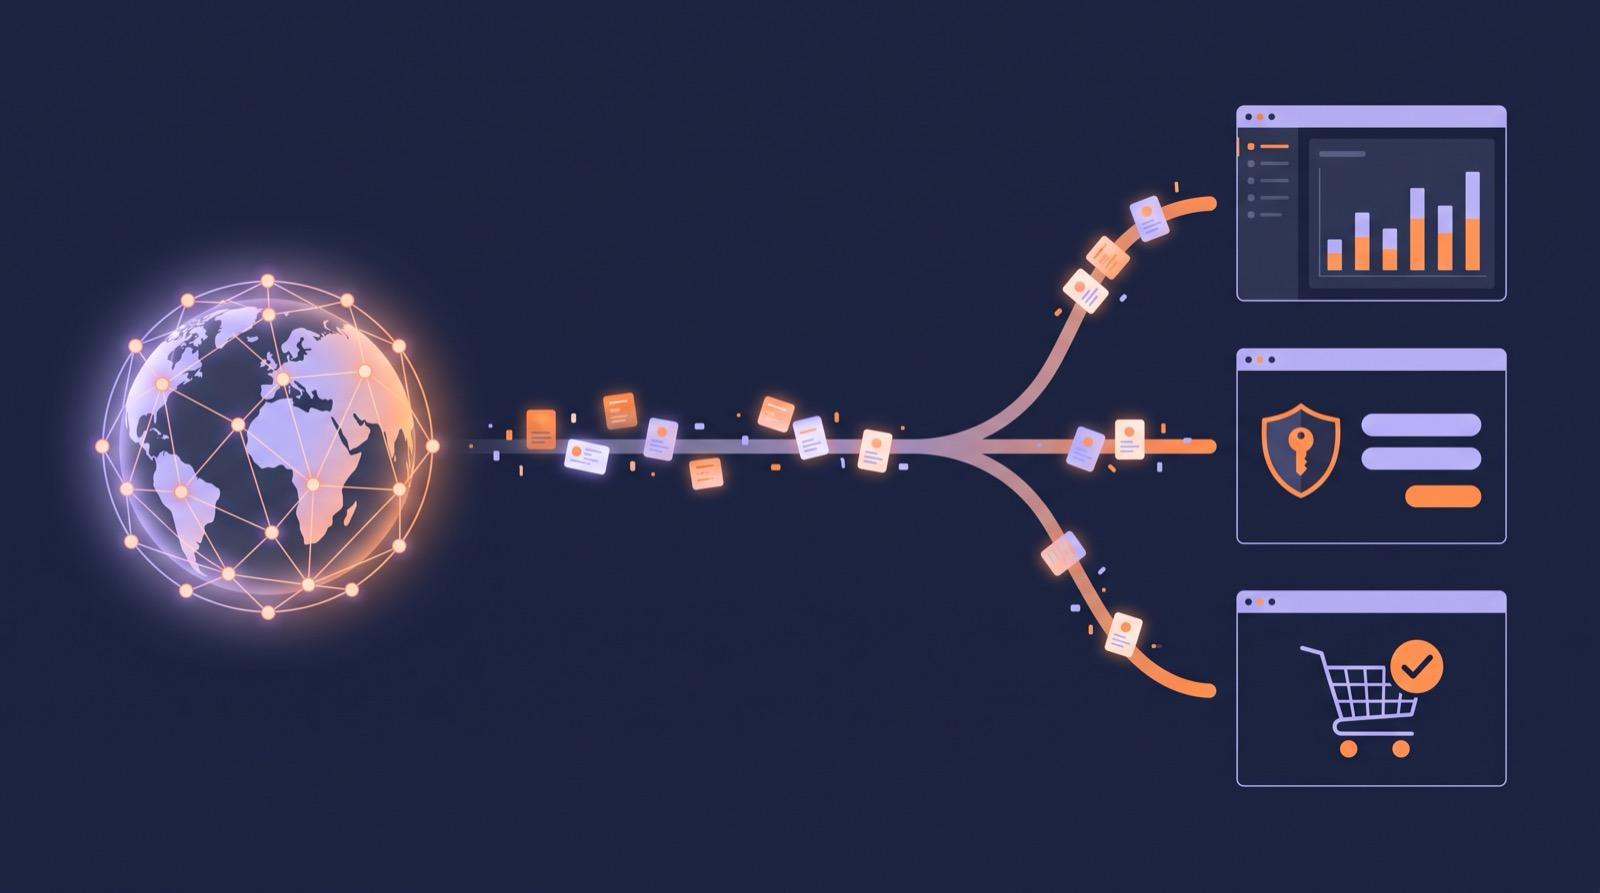
Most of the tools that make decisions on inbound traffic already speak the same threat intelligence standard: TAXII. Microsoft Sentinel, Splunk Enterprise Security, Elastic Security, Cortex XSOAR and OpenCTI all import TAXII feeds natively. So that’s how CrowdSec delivers its IP reputation: a TAXII 2.1 feed of STIX 2.1 indicators, updated every hour, that any of these platforms can subscribe to in minutes, with no custom integration.
Each indicator tells you whether an IP is malicious or suspicious, how confident we are, what it was doing, and what kind of connection it is: residential, data center, VPN, Tor or proxy. You match it against sign-ins, transactions, firewall and web logs, and decide what to let in.
This guide covers what’s in the feed, how to connect it, and four use cases where it changes a decision on inbound traffic.
What TAXII and STIX are, in one minute
- STIX (Structured Threat Information Expression) is the standard format for threat intelligence: a common way to describe an indicator, an IP for example, with its context.
- TAXII (Trusted Automated eXchange of Intelligence Information) is the standard protocol to share it over HTTPS: a client asks a server for a “collection” and pulls the new objects at regular intervals.
Both are OASIS open standards. Their value is that you integrate once: a SIEM or threat intelligence platform that reads one TAXII feed reads them all. Microsoft Sentinel, for instance, imports from any TAXII 2.0 or 2.1 server through its built-in “Threat Intelligence – TAXII” data connector.
What’s in the CrowdSec TAXII feed
Our TAXII server implements TAXII 2.1 and publishes the CTI in a single collection, real-time-feeds, updated hourly. Every IP becomes one STIX indicator (a full example is in our TAXII documentation):
| Field | What it tells you |
|---|---|
pattern |
The IP (IPv4 or IPv6), in the STIX pattern your SIEM matches against logs |
indicator_types |
Our verdict: malicious-activity, anomalous-activity (suspicious) or unknown |
confidence |
How sure we are, from 0 to 100: use it as a threshold in your rules |
labels |
The context: reputation, behaviors (http:bruteforce, ssh:bruteforce, http:exploit…), classifications and list memberships |
created / modified |
First and last time our network saw the IP |
valid_from / valid_until |
The validity window: indicators expire, so an IP that stops attacking leaves your feed |
The classifications are where the decisions get interesting. The ones that matter most for inbound traffic:
| Label | Meaning |
|---|---|
connection-type:residential |
The IP belongs to a residential connection |
connection-type:data-center |
The IP belongs to a data center |
proxy:vpn |
The IP exposes a VPN service or is flagged as one |
proxy:tor |
Tor exit node |
proxy:icloud-private-relay |
Apple iCloud Private Relay |
crowdsec:ai_vpn_proxy |
Flagged as a VPN or proxy by CrowdSec’s AI detection |
profile:corporate-proxy |
A corporate proxy exit point |
ai-crawler:, ai-search: |
AI companies’ crawlers and AI search agents, by company |
bot:fake_browser |
Claims to be a browser but doesn’t behave like one |
(Full list: classifications.)
Everyone gets the same feed. To keep only what matters to you (say, proxies and VPNs for an identity team), filter on these labels when you ingest, or in your detection rules.
Where the labels come from: attacks seen by our network of more than 300,000 active Security Engines on real production servers, which is why the feed knows about targeted attacks as well as internet-wide scanning.
TAXII, API or offline replica: which one when?
We deliver the same intelligence three ways. Pick by where the decision happens.
| TAXII feed | CTI API | Offline replica | |
|---|---|---|---|
| How | Your platform polls our TAXII server and pulls what changed | You ask about one IP (or a batch) when you need it | You get the full database as a file |
| Best for | Keeping a SIEM or TIP in sync, matching every log line locally | Enriching one alert, a playbook step, an analyst’s lookup | Air-gapped sites, in-app checks with zero latency |
| Context | Verdict, confidence, behaviors, classifications | Everything we know: 30+ fields, scores, targeted countries and industries, MITRE techniques | Full |
| Freshness | Hourly | Live | Synced every hour on your side |
They combine well: TAXII to match everything in bulk, the API to get the full story on the few matches that raise an alert.
Use case 1: settle the doubt on an Entra ID sign-in (Microsoft Sentinel, Defender portal)
Take a successful Entra ID sign-in from an IP you’ve never seen for that user: residential, abroad, at night. Here’s how the feed settles it in Microsoft Sentinel (in the Azure portal or, after 31 March 2027, only in the Microsoft Defender portal).
1. Connect the feed. In Sentinel, install the Threat Intelligence solution, open the Threat Intelligence – TAXII data connector and fill in:
| Connector field | Value |
|---|---|
| API root URL | https://taxii.cti.api.crowdsec.net/v1/cti/ |
| Collection ID | real-time-feeds |
| Username | any non-empty value, for example crowdsec |
| Password | your CrowdSec TAXII API key |
| Polling frequency | hourly, to match our refresh |
Within minutes, CrowdSec indicators appear in Sentinel’s threat intelligence pane.
2. Turn on matching. Microsoft ships ready-made analytics rules that map threat intelligence IPs to your logs. “TI Map IP Entity to SigninLogs” checks interactive and non-interactive Entra ID sign-ins every hour against your indicators, and it accepts the TAXII connector as its source. Enable it, and filter on the indicator’s confidence and labels if you want to act differently on a residential proxy and on a Tor exit node.
3. Decide. A match creates an incident; an automation rule runs a playbook. Microsoft’s Entra ID playbooks cover the usual responses:
| What the feed says about the sign-in IP | A sensible response |
|---|---|
Malicious, with http:bruteforce or credential-stuffing behaviors |
Revoke sessions (Revoke-AADSignInSessions), reset the password (Reset-AADUserPassword) |
proxy:vpn, crowdsec:ai_vpn_proxy or residential with attack behaviors, user never seen there |
Ask the user (Prompt-User), or mark them risky (Confirm-EntraIDRiskyUser) so your risk-based Conditional Access policies take over |
connection-type:data-center on a human user’s sign-in |
Investigate: people rarely log in from a cloud provider |
proxy:tor |
Block, if your policy doesn’t allow Tor |
The same rule family exists for other Microsoft logs: Microsoft 365 activity (OfficeActivity), Defender for Endpoint network events (DeviceNetworkEvents), Defender for Cloud Apps (CloudAppEvents), Azure Firewall, Key Vault, Azure SQL and IIS logs. One feed covers them all.
Prefer a lookup per sign-in? Our Sentinel playbook calls the CTI API on each successful Entra ID authentication and raises an alert when the IP is malicious or suspicious. It’s the API route, with the full context for every alert.
Use case 2: fraud prevention, or is this customer really a customer?
Fraud rings rent residential proxies so their traffic looks like your customers’, and run bots from data centers when speed matters more than stealth. In our SANS 2026 data, 68.85% of attacking IPs were residential and 24.79% came from data centers, the rest from proxies, VPNs, AI infrastructure and Tor. Blocking “data center IPs” alone leaves most of it through.
What the feed adds at sign-up, login or checkout:
- Connection type: a residential IP with attack behaviors is the signature of a residential proxy exit used for abuse, the hardest kind to spot any other way.
- Anonymizers:
proxy:vpn,proxy:tor,proxy:icloud-private-relay,crowdsec:ai_vpn_proxy. - History: first and last seen, and what the IP did elsewhere (credential stuffing, scraping, exploitation).
Use it as a risk signal rather than a verdict. Residential and mobile IPs are shared (several households can sit behind one address), so the right response is usually a step-up: CAPTCHA, extra verification, 3-D Secure, manual review. Keep the hard blocks for high-confidence malicious IPs. Fraud engines that need an answer in milliseconds usually load the offline replica or a TAXII-synced list locally, instead of calling an API on every request.
Use case 3: enrich your SIEM and cut triage time
Most SOC alerts with an IP in them come from somewhere: a VPN gateway, a WAF, an IDS, an EDR flagging a connection. With the feed in your SIEM, every one of those alerts arrives already tagged with a verdict, a confidence score and what the IP was doing elsewhere. Analysts stop opening five tabs, and your rules can raise or lower severity automatically.
Platforms with native TAXII 2.x import, per their own documentation:
| Platform | Where |
|---|---|
| Microsoft Sentinel | Threat Intelligence – TAXII data connector (TAXII 2.0 and 2.1) |
| Splunk Enterprise Security 8 | Configure → Threat intelligence → New TAXII 2 feed |
| Elastic Security | Custom Threat Intelligence integration (TAXII 2.x client, STIX 2.1 mapped to ECS) |
| Palo Alto Cortex XSOAR | TAXII 2 Feed integration (TAXII 2.0 and 2.1) |
| OpenCTI | TAXII 2 connector |
| Threat intelligence platforms (Anomali and others) | Their TAXII client |
Already on our API integrations for Splunk, QRadar, Cortex XSOAR, MISP, OpenCTI, TheHive or Sekoia? Keep them for on-demand lookups; TAXII adds bulk matching on top.
Use case 4: decide at the edge (know first, then block)
TAXII is how intelligence reaches the tools that decide: SIEMs, SOAR playbooks, identity and fraud engines. Firewalls are built to block, and most of them don’t speak TAXII. For them, CrowdSec serves the same data as IP threat feeds your firewall pulls on its own (Palo Alto External Dynamic Lists, FortiGate threat feeds, Check Point IoC feeds and others).
A simple split works for most teams: the TAXII feed in the SIEM to know and decide, a curated blocklist on the firewall to stop the obvious at the door, so it never becomes an alert in the first place.
Set it up in 15 minutes
- Get a TAXII key. The feed is a Premium feature with a dedicated API key: talk to us.
- Check access with one command:
curl -u "crowdsec:$API_KEY" https://taxii.cti.api.crowdsec.net/v1/cti/collections/ - Point your TAXII client at the API root
https://taxii.cti.api.crowdsec.net/v1/cti/and the collectionreal-time-feeds. Basic authentication: any username, your key as the password (or thex-api-keyheader). - Poll hourly. Clients that support it pull only what changed with
added_after, and follow thenextcursor through pages. - Respect
valid_until. Expired indicators should drop out of your matching, so an IP that stopped attacking stops triggering. - Write the rules: start with sign-ins, VPN and WAF logs, where an IP reputation hit changes a decision.
What it can’t do
IP reputation answers one question very well: what is this IP, and what has it been doing? It doesn’t carry phishing domains, malware hashes or threat actor profiles (we wrote about where IP reputation stops and full CTI starts). It knows the IPs that attack internet-facing systems, so it says nothing about what happens inside your network. And shared IPs deserve care: treat residential and mobile matches as signals that trigger a check, with hard blocks reserved for high-confidence malicious IPs.
FAQ
Does CrowdSec provide a TAXII feed? Yes. CrowdSec’s TAXII server implements TAXII 2.1 and serves IP reputation as STIX 2.1 indicators in the real-time-feeds collection, updated hourly. It’s a Premium feature with a dedicated API key.
Can I use CrowdSec threat intelligence in Microsoft Sentinel? Yes, two ways: connect the TAXII feed with Sentinel’s Threat Intelligence – TAXII data connector and use Microsoft’s “TI Map IP Entity” analytics rules, or deploy the CrowdSec Sentinel playbook, which looks up IPs through the CrowdSec CTI API.
Can Entra ID use CrowdSec IP reputation? Through Microsoft Sentinel: sign-in logs are matched against CrowdSec indicators, and a playbook can revoke sessions, reset a password, prompt the user, or mark them risky in Entra ID Protection so risk-based Conditional Access applies.
How can I tell if an IP is a residential proxy, a VPN or a data center? CrowdSec labels each IP with its connection type (connection-type:residential or connection-type:data-center) and anonymizer classifications such as proxy:vpn, proxy:tor and crowdsec:ai_vpn_proxy. A residential IP with attack behaviors is a strong sign of a residential proxy used for abuse. You can check any IP for free in the CrowdSec IP lookup.
Is there a free CrowdSec TAXII feed? The TAXII feed requires a dedicated Premium key. For free, you can look up any IP in the console and get 120 CTI API lookups a month with a free key.
What’s the difference between the TAXII feed and the CrowdSec API? TAXII keeps your SIEM or threat intelligence platform in sync with our indicators, so matching happens locally at any volume. The API answers questions about specific IPs on demand, with the full context (30+ fields). Most teams use both.
Try it
- Check a few IPs from your own sign-in or VPN logs in the free CrowdSec IP lookup, or run IPDEX on a whole log file.
- Ready to connect your SIEM? Get a TAXII key.
By Philippe Humeau, CEO, CrowdSec