What 500,000 servers saw: 8 lessons on exploitation from SANS 2026
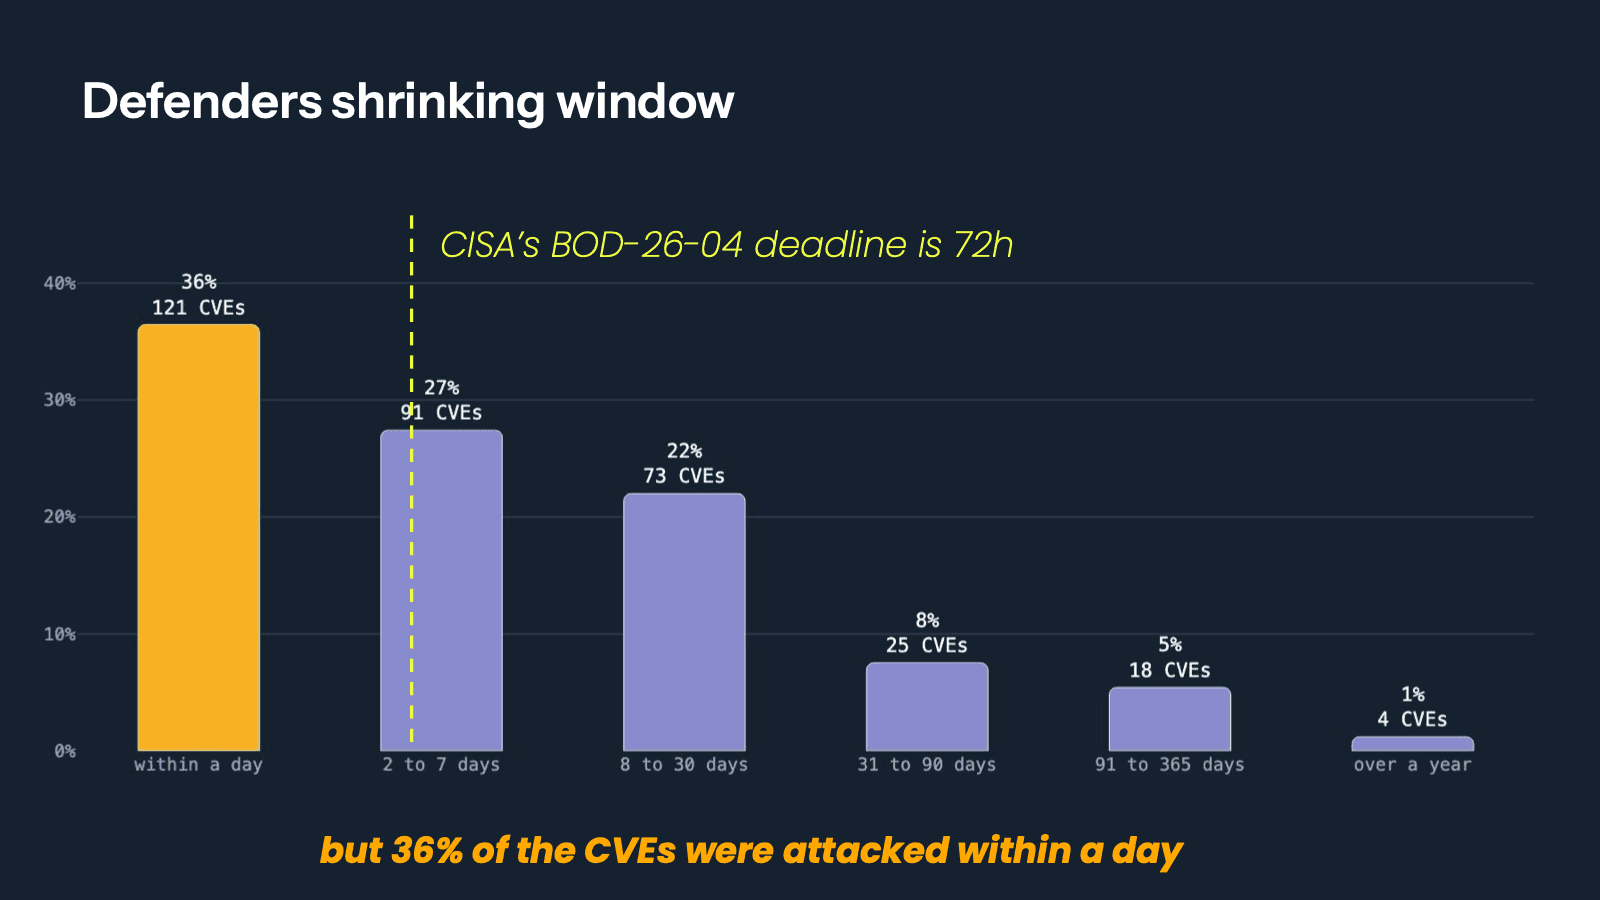
36% of exploited CVEs were attacked within a day of publication. What 500,000 servers saw at SANS 2026: borrowed cloud IPs, early zero-days, old CVEs.
Proactive Cybersecurity
IP reputation vs full CTI: what your SOC actually needs
Most SOCs need fast IP reputation in their SIEM before they need attribution-heavy CTI. How to tell them apart, and what to ask any IP reputation vendor.
CrowdSec
5 years of CrowdSec Data Science: What Our Code Really Shows
CrowdSec data scientist looks back on 5 years: how we count our network, why we run honeypots, canaries in blocklists, and what the code leak really shows.
How MindMax Neutralized a Massive Bot Scraping Attack with CrowdSec WAF Bot Detection
Discover how Finnish company MindMax used the new CrowdSec WAF bot detection feature to stop a massive, highly distributed residential botnet targeting their dictionary sites.
CrowdSec
The PaperPhone Cluster: One Operator, 80K IPs, 43 countries
CrowdSec bot detection uncovered PaperPhone, a coordinated headless browser network using 75,000 IPs across 43 countries and fabricated mobile identities.
Integrations
CrowdSec vs Suricata: Do You Need Both for Linux Servers?
See if CrowdSec’s IP blocking or Suricata’s deep inspection fits your Linux server. Avoid alert fatigue with the right enforcement strategy.
Announcement
Analyse de l’attaque de la supply chain TanStack
Philippe Humeau, PDG de CrowdSec, revient en détail sur l’attaque de la chaîne d’approvisionnement de 2026, depuis la fuite du code source et l’enquête technique jusqu’aux enseignements tirés.
Announcement
TanStack Supply Chain Attack Analysis
CrowdSec CEO Philippe Humeau shares the full story behind the 2026 supply chain attack, from the source code leak and forensic investigation to the lessons learned.
Announcement
CrowdSec Statement: Source Code Exposure in May 2026
CrowdSec update on a source code exposure that occurred in May 2026, including the scope, impact, investigation, and security measures taken.
AI
How to Block Bots, Headless Browsers, and Scrapers on Nginx with CrowdSec
Set up open-source Nginx bot protection with CrowdSec to block scrapers, headless browsers, AI crawlers, and other unwanted automated traffic.
AI
What’s New in CrowdSec 1.8: WAF Bot Detection, Kubernetes Datasource, and Performance Improvements
Discover what’s new in CrowdSec 1.8, including WAF bot detection, a dedicated Kubernetes datasource, faster LAPI synchronization, and improved Console alerts.
AI
Why You Should Write a Skill for Your Software
Learn why AI agent skills make software setup more reliable, reduce LLM guesswork, improve troubleshooting, and can even expose gaps in your documentation.
Integrations
WAF for Traefik with CrowdSec: Virtual Patching in Docker
Add an open-source WAF to Traefik with CrowdSec. Wire the bouncer plugin, enable virtual patching, and block real attacks, step by step in Docker.
Integrations
Open-Source WAF for Nginx on Ubuntu with CrowdSec
Deploy an open-source WAF for Nginx on Ubuntu with CrowdSec. Install the AppSec component, enable virtual patching, and block attacks step by step
Proactive Cybersecurity
CISA gives you 3 days to patch and triage. Live Exploit Tracker gives you a head start
CISA BOD 26-04 mandates risk-based patching driven by real exploitation evidence. Live Exploit Tracker delivers that evidence live — per CVE, per vendor.
Product Updates
CrowdSec 1.7.8 Security Release: Fixes High-Severity WAF Bypass and LAPI DoS Vulnerabilities
CrowdSec 1.7.8 fixes two security vulnerabilities: CVE-2026-44982, a high-severity WAF bypass, and CVE-2026-44981, a Local API denial-of-service issue. Upgrade now.
CrowdSec
Edge is the new endpoint: How to respond when edge CVEs go hot
Edge CVEs move fast from disclosure to exploitation. Learn a practical 60-minute response framework to assess exposure, reduce risk, deploy mitigations, and communicate clearly during edge vulnerability incidents.
Success Story
ButanGas Enhances Cybersecurity with CrowdSec to Protect LPG Distribution
ButanGas strengthens its IT security using CrowdSec’s real-time threat intelligence & blocklists, ensuring secure, uninterrupted LPG distribution across Italy.
Tutorial
Protecting Your Web Applications with OWASP CRS and CrowdSec
Deploy the OWASP Core Rule Set (CRS) with CrowdSec to detect SQL injection, XSS, and other attack patterns. Learn how to install, tune, and enable blocking.
Inside CrowdSec
The future of CrowdSec support in Kubernetes
Explore CrowdSec support for Kubernetes, Ingress-NGINX deprecation, and how to migrate to Gateway API using Traefik, HAProxy, and Envoy.
Learn the difference between vulnerabilities, threats, and risks, and how understanding their lifecycle helps prevent security incidents.
Proactive Cybersecurity
What 500,000 servers saw: 8 lessons on exploitation from SANS 2026
36% of exploited CVEs were attacked within a day of publication. What 500,000 servers saw at SANS 2026: borrowed cloud IPs, early zero-days, old CVEs.
Proactive Cybersecurity
IP reputation vs full CTI: what your SOC actually needs
Most SOCs need fast IP reputation in their SIEM before they need attribution-heavy CTI. How to tell them apart, and what to ask any IP reputation vendor.
5 years of CrowdSec Data Science: What Our Code Really Shows
CrowdSec data scientist looks back on 5 years: how we count our network, why we run honeypots, canaries in blocklists, and what the code leak really shows.
Success Story
How MindMax Neutralized a Massive Bot Scraping Attack with CrowdSec WAF Bot Detection
Discover how Finnish company MindMax used the new CrowdSec WAF bot detection feature to stop a massive, highly distributed residential botnet targeting their dictionary sites.
CrowdSec
The PaperPhone Cluster: One Operator, 80K IPs, 43 countries
CrowdSec bot detection uncovered PaperPhone, a coordinated headless browser network using 75,000 IPs across 43 countries and fabricated mobile identities.
Integrations
CrowdSec vs Suricata: Do You Need Both for Linux Servers?
See if CrowdSec’s IP blocking or Suricata’s deep inspection fits your Linux server. Avoid alert fatigue with the right enforcement strategy.
Announcement
Analyse de l’attaque de la supply chain TanStack
Philippe Humeau, PDG de CrowdSec, revient en détail sur l’attaque de la chaîne d’approvisionnement de 2026, depuis la fuite du code source et l’enquête technique jusqu’aux enseignements tirés.
Announcement
TanStack Supply Chain Attack Analysis
CrowdSec CEO Philippe Humeau shares the full story behind the 2026 supply chain attack, from the source code leak and forensic investigation to the lessons learned.
Announcement
CrowdSec Statement: Source Code Exposure in May 2026
CrowdSec update on a source code exposure that occurred in May 2026, including the scope, impact, investigation, and security measures taken.
AI
How to Block Bots, Headless Browsers, and Scrapers on Nginx with CrowdSec
Set up open-source Nginx bot protection with CrowdSec to block scrapers, headless browsers, AI crawlers, and other unwanted automated traffic.
AI
What’s New in CrowdSec 1.8: WAF Bot Detection, Kubernetes Datasource, and Performance Improvements
Discover what’s new in CrowdSec 1.8, including WAF bot detection, a dedicated Kubernetes datasource, faster LAPI synchronization, and improved Console alerts.
AI
Why You Should Write a Skill for Your Software
Learn why AI agent skills make software setup more reliable, reduce LLM guesswork, improve troubleshooting, and can even expose gaps in your documentation.
Integrations
WAF for Traefik with CrowdSec: Virtual Patching in Docker
Add an open-source WAF to Traefik with CrowdSec. Wire the bouncer plugin, enable virtual patching, and block real attacks, step by step in Docker.
Integrations
Open-Source WAF for Nginx on Ubuntu with CrowdSec
Deploy an open-source WAF for Nginx on Ubuntu with CrowdSec. Install the AppSec component, enable virtual patching, and block attacks step by step
Proactive Cybersecurity
CISA gives you 3 days to patch and triage. Live Exploit Tracker gives you a head start
CISA BOD 26-04 mandates risk-based patching driven by real exploitation evidence. Live Exploit Tracker delivers that evidence live — per CVE, per vendor.
Product Updates
CrowdSec 1.7.8 Security Release: Fixes High-Severity WAF Bypass and LAPI DoS Vulnerabilities
CrowdSec 1.7.8 fixes two security vulnerabilities: CVE-2026-44982, a high-severity WAF bypass, and CVE-2026-44981, a Local API denial-of-service issue. Upgrade now.
CrowdSec
Edge is the new endpoint: How to respond when edge CVEs go hot
Edge CVEs move fast from disclosure to exploitation. Learn a practical 60-minute response framework to assess exposure, reduce risk, deploy mitigations, and communicate clearly during edge vulnerability incidents.
Success Story
ButanGas Enhances Cybersecurity with CrowdSec to Protect LPG Distribution
ButanGas strengthens its IT security using CrowdSec’s real-time threat intelligence & blocklists, ensuring secure, uninterrupted LPG distribution across Italy.
Tutorial
Protecting Your Web Applications with OWASP CRS and CrowdSec
Deploy the OWASP Core Rule Set (CRS) with CrowdSec to detect SQL injection, XSS, and other attack patterns. Learn how to install, tune, and enable blocking.
Inside CrowdSec
The future of CrowdSec support in Kubernetes
Explore CrowdSec support for Kubernetes, Ingress-NGINX deprecation, and how to migrate to Gateway API using Traefik, HAProxy, and Envoy.